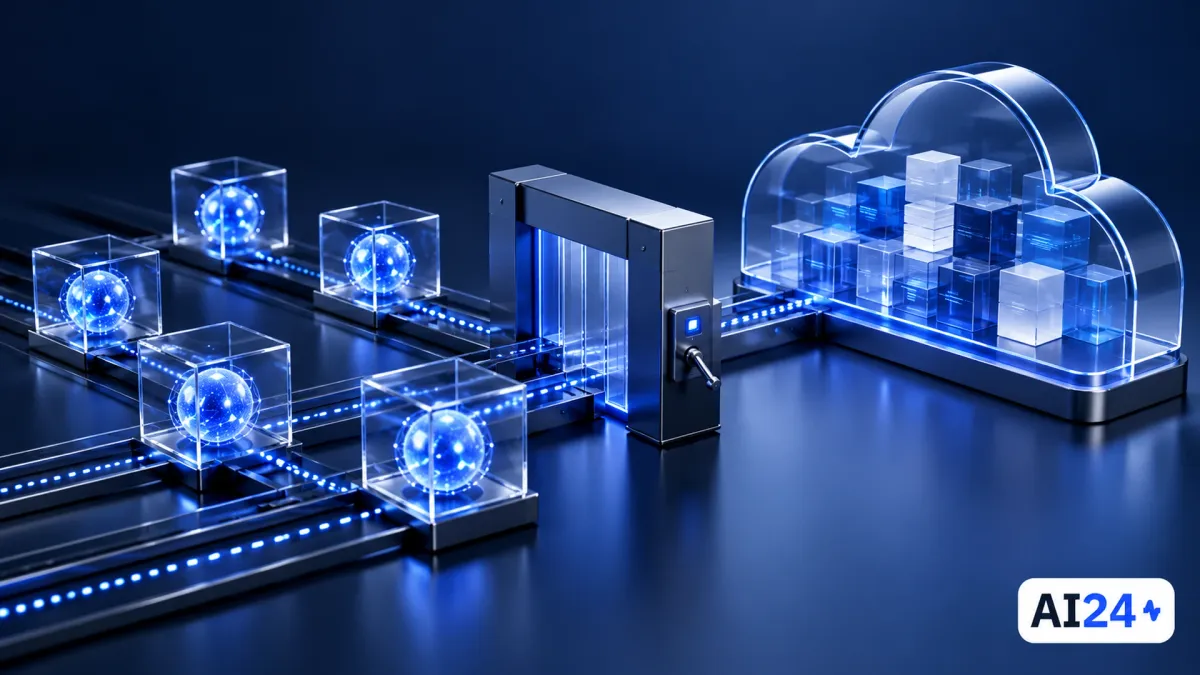
Israel's NanoCo is developing security, governance and control layers around AI agents that act on employees' behalf. In an October 28, 2026 report in The Jerusalem Post, the company described combining agent isolation with an external approval gateway. The aim is to let the system do organizational work without giving it unrestricted access to all an employee's data and tools.
Brothers Gavriel Cohen, CEO and product development lead, and Lazar Cohen, responsible for commercial operations, founded the company. It is backed by a 12 million dollar seed round led by Valley Capital Partners, with Docker, Vercel and monday.com participating. That round was already reported in May 2026. October's coverage adds product and usage detail; it does not itself establish a new round.
The agent prepares, a person decides what leaves
NanoCo says an enterprise agent needs to work with email, calendars, customer relationship management, service systems and code repositories. These are not merely general information sources. Actions can affect a customer, an internal document or communications sent on an employee's behalf. The question therefore extends beyond the quality of the model's answer.
The company website describes agents preparing drafts and preliminary work, with sensitive actions requiring human approval under organizational policy. For a message, the distinction is between composing it and permission to send it. That is an operational difference: a generated draft is not a delivered message, even when both begin with the same user request.
The Jerusalem Post describes a gateway outside the agent environment. Requests such as accessing information or sending communications pass through it for a person to approve or deny. Its external position matters: the authorization decision is not left solely to the system trying to complete the task. NanoCo presents this as a control layer around agent capabilities, rather than an instruction to behave cautiously.
What NanoClaw's isolation adds
NanoClaw is the company's open-source platform. Its repository describes agents running in separate Linux containers with filesystem isolation. The idea is to define a boundary between an agent's working environment and other resources. This differs from a conversational instruction not to open a certain file: it is part of the runtime where actions occur.
Isolation and the approval gateway address different questions. Isolation determines which resources are within the agent environment's reach; the gateway handles requests crossing that boundary that need authorization. The arrangement combines a defined workspace with rules for moving beyond it. Neither component alone describes the entire organization's access policy.
NanoCo says agents operate without credentials inside them, and sensitive actions are audited under organization-controlled policies. These are company-described design features, not a guarantee that every deployment is equally secure. Tool permissions, connected information and how people approve requests remain part of real-world operation.
From open source to the customer's cloud
NanoCo's commercial offering can run inside a customer's AWS, GCP or Azure account, according to its website. The company presents this as combining personal employee context with centralized access control and governance. Moving from an individually operated assistant to a team-wide system also raises the question of who manages permissions over time.
The company describes an assistant embedded in existing work environments, such as Slack or Teams, that learns employee context. Accumulated context can make recurring tasks more convenient, but also makes control over stored information and its use integral to the product. NanoCo says the knowledge built belongs to, and is controlled by, the user.
Customer-cloud deployment should not imply that every connected service and data route is identical in every installation. Email systems, models and work tools can be separate workflow components. The deployment description explains where the enterprise system can operate; it does not replace configuration of each organization's connections and permissions. The website offers early access rather than a uniform public price list.
A 12 million dollar round, with a clear timeline
CTech reported the seed round led by Valley Capital Partners on May 20, 2026, including Docker, Vercel and monday.com. October's report repeats that amount and those investors. Preserving chronology matters: the same amount appearing in later coverage is no basis for adding two rounds together or doubling the stated funding total.
Lazar Cohen told The Jerusalem Post that the idea grew from the brothers' previous work with automation and agents, and concerns about connecting them to sensitive business information without sufficient controls. This explains the focus on operating and permission layers around agents. The product is presented as infrastructure governing access and action, not as a new language model.
Open-source interest is part of the business backdrop. October's report cites more than 30,000 GitHub stars. Stars indicate interest among platform users, not paying customers or active enterprise deployments. Technology companies' participation in a funding round does not itself mean each has deployed the product to every employee.
Permission boundaries become part of the product
As an agent gains tools, both its potential usefulness and range of possible actions increase. A system that only summarizes information differs from one that reads records, drafts a message and sends it outside. NanoCo is trying to combine useful employee work with an organization's ability to decide which actions are permitted and under what conditions.
The practical distinction is between an agent's reasoning quality and its authority. A model can suggest the right action without permission to execute it, or make a mistake on an apparently simple task. Isolation, human approval and auditing do not necessarily improve every answer, but define the framework in which answers can become actions on an organization's behalf.